


08-26-2026, 09:04 PM
(This post was last modified: 10-21-2026, 10:02 AM by Sir-Vigu.
Edit Reason: Versioned Vault repair and scoped test evidence — 21 October 2026
)
Verification record: DFV-AUDIT-20261021
Repair wave 2 — DF Login OTP 2.0.0
21 October 2026 · Sir-Vigu · Scoped staging checks passed
Security-focused replacement for the recovered 1.2 distribution. This is a versioned repair/rebuild, not a recovered original archive. No production activation was performed.
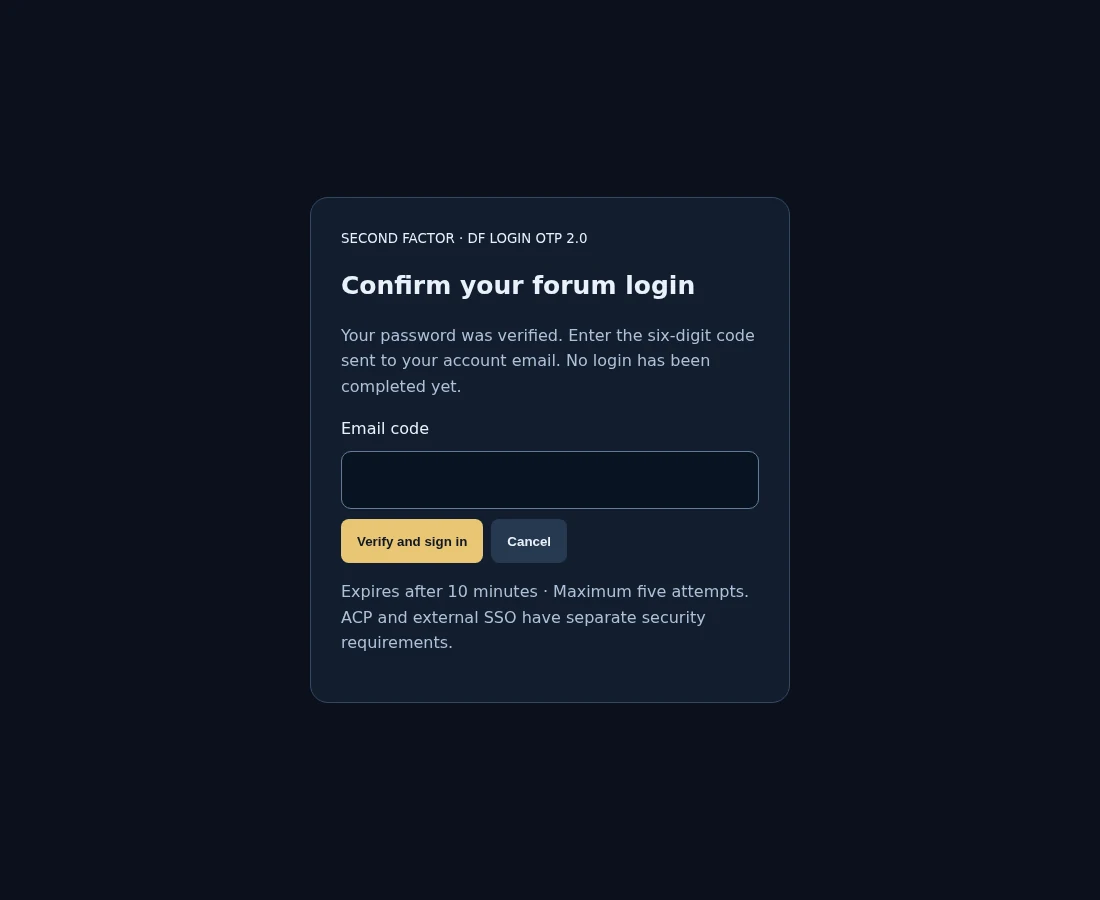
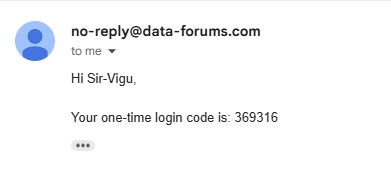
Actual isolated MyBB test capture. Sample data; not a production install or a real payment/broadcast claim.
What changed
Requirements
MyBB 1.8.40 tested; PHP 8.1+ intended (runtime tests on 8.4.26); MySQL/MariaDB; modern browser. Custom themes, external authentication, mail and provider integrations require their own staging checks.
Installation and upgrade
Back up first. Upload inc/ and jscripts/ into the MyBB root. Keep an authenticated ACP recovery session open. Back up DB/files. Deactivate 1.2 without uninstalling, upload the new PHP, then Install & Activate 2.0 to create the new challenge/key tables. Confirm group IDs, HTTPS and real mail delivery before ending the recovery session. Legacy OTP page templates are unused; do not downgrade without restoring the backup.
Settings
ACP → Settings → DF Login OTP. Protected groups defaults to 4,6 on fresh installation. Review existing group values on upgrade. Require HTTPS must stay Yes in production.
Usage
Test evidence
21 browser/auth-flow assertions cover correct/incorrect code, no auth before OTP, CSRF, expiry, replay, session transfer, credential change, cancellation, attempts, HTTP refusal, delivery failure and ordinary-member login. Additional PHP checks cover protected primary/additional groups.
The eight-release wave passed 117 scoped assertions across PHP/MyBB, browser, HTTP and lifecycle checks. Some tests used a combined plugin context; this is not a universal compatibility certificate or an independent security audit.
Limitations / breaking changes
Protects native forum login completion, NOT the Admin CP login or SSO plugins that set authentication cookies directly. Preserve and test separate ACP/SSO security. Email delivery was exercised through a lab capture adapter, not your real SMTP provider. Third-party CAPTCHA/login integrations need staging checks. This is not an independent security audit.
Deactivate / uninstall
Deactivate retains settings/challenges. Uninstall removes the new challenge/key tables and its settings, invalidating pending challenges; it does not delete accounts or posts.
Changelog
2.0.0 — 21 October 2026: Security-focused replacement for the recovered 1.2 distribution. Full source, README, upgrade notes, changelog, test-scope note and licence included in the ZIP.
Download the current Vault release — existing access rules apply.
Support / licence
Reply below or PM Sir-Vigu (uid 1) with versions and a minimal reproduction. Never publish credentials or private member data. GPL-3.0-or-later; existing attribution retained.
Full verification register
Original release notes
🔐 DF Login OTP v1.2
Bank-style email two-factor for your staff logins - 🎁 FREE for all members
🔧 What it is
Email two-factor authentication for the logins you choose (admins/mods by default). A stolen password is worthless without the inbox. Everyone else logs in exactly as before.
🔁 How it works
🏗️ Structure (reviewer standard)
Lifecycle-only main file · hooks.php · handlers.php · permissions.php · db.php (schema-less, documented) · settings.json/php (insert_query_multiple) · templates.json/php · external stylesheet · English + ACP language packs.
📦 Inside
Full plugin tree - download from the DF Vault button below.
🛠️ Install
Reply here or PM Sir-Vigu.
A Data-Forums free release - tested on ourselves before sharing. data-forums.com
Repair wave 2 — DF Login OTP 2.0.0
21 October 2026 · Sir-Vigu · Scoped staging checks passed
Security-focused replacement for the recovered 1.2 distribution. This is a versioned repair/rebuild, not a recovered original archive. No production activation was performed.
Actual isolated MyBB test capture. Sample data; not a production install or a real payment/broadcast claim.
What changed
- The hook runs after native MyBB password validation and before the authentication cookie is issued.
- Random opaque pending token; keyed code hashes, session binding, ten-minute expiry and five-attempt limit stored server-side.
- One-use conditional consumption, password/loginkey-change invalidation, cancellation and request limits.
- Primary and additional protected groups count. HTTPS is required by default.
- Mail-adapter failure fails closed; no password, encrypted password token or plaintext code is stored in challenge records.
Requirements
MyBB 1.8.40 tested; PHP 8.1+ intended (runtime tests on 8.4.26); MySQL/MariaDB; modern browser. Custom themes, external authentication, mail and provider integrations require their own staging checks.
Installation and upgrade
Back up first. Upload inc/ and jscripts/ into the MyBB root. Keep an authenticated ACP recovery session open. Back up DB/files. Deactivate 1.2 without uninstalling, upload the new PHP, then Install & Activate 2.0 to create the new challenge/key tables. Confirm group IDs, HTTPS and real mail delivery before ending the recovery session. Legacy OTP page templates are unused; do not downgrade without restoring the backup.
Settings
ACP → Settings → DF Login OTP. Protected groups defaults to 4,6 on fresh installation. Review existing group values on upgrade. Require HTTPS must stay Yes in production.
Usage
Code:
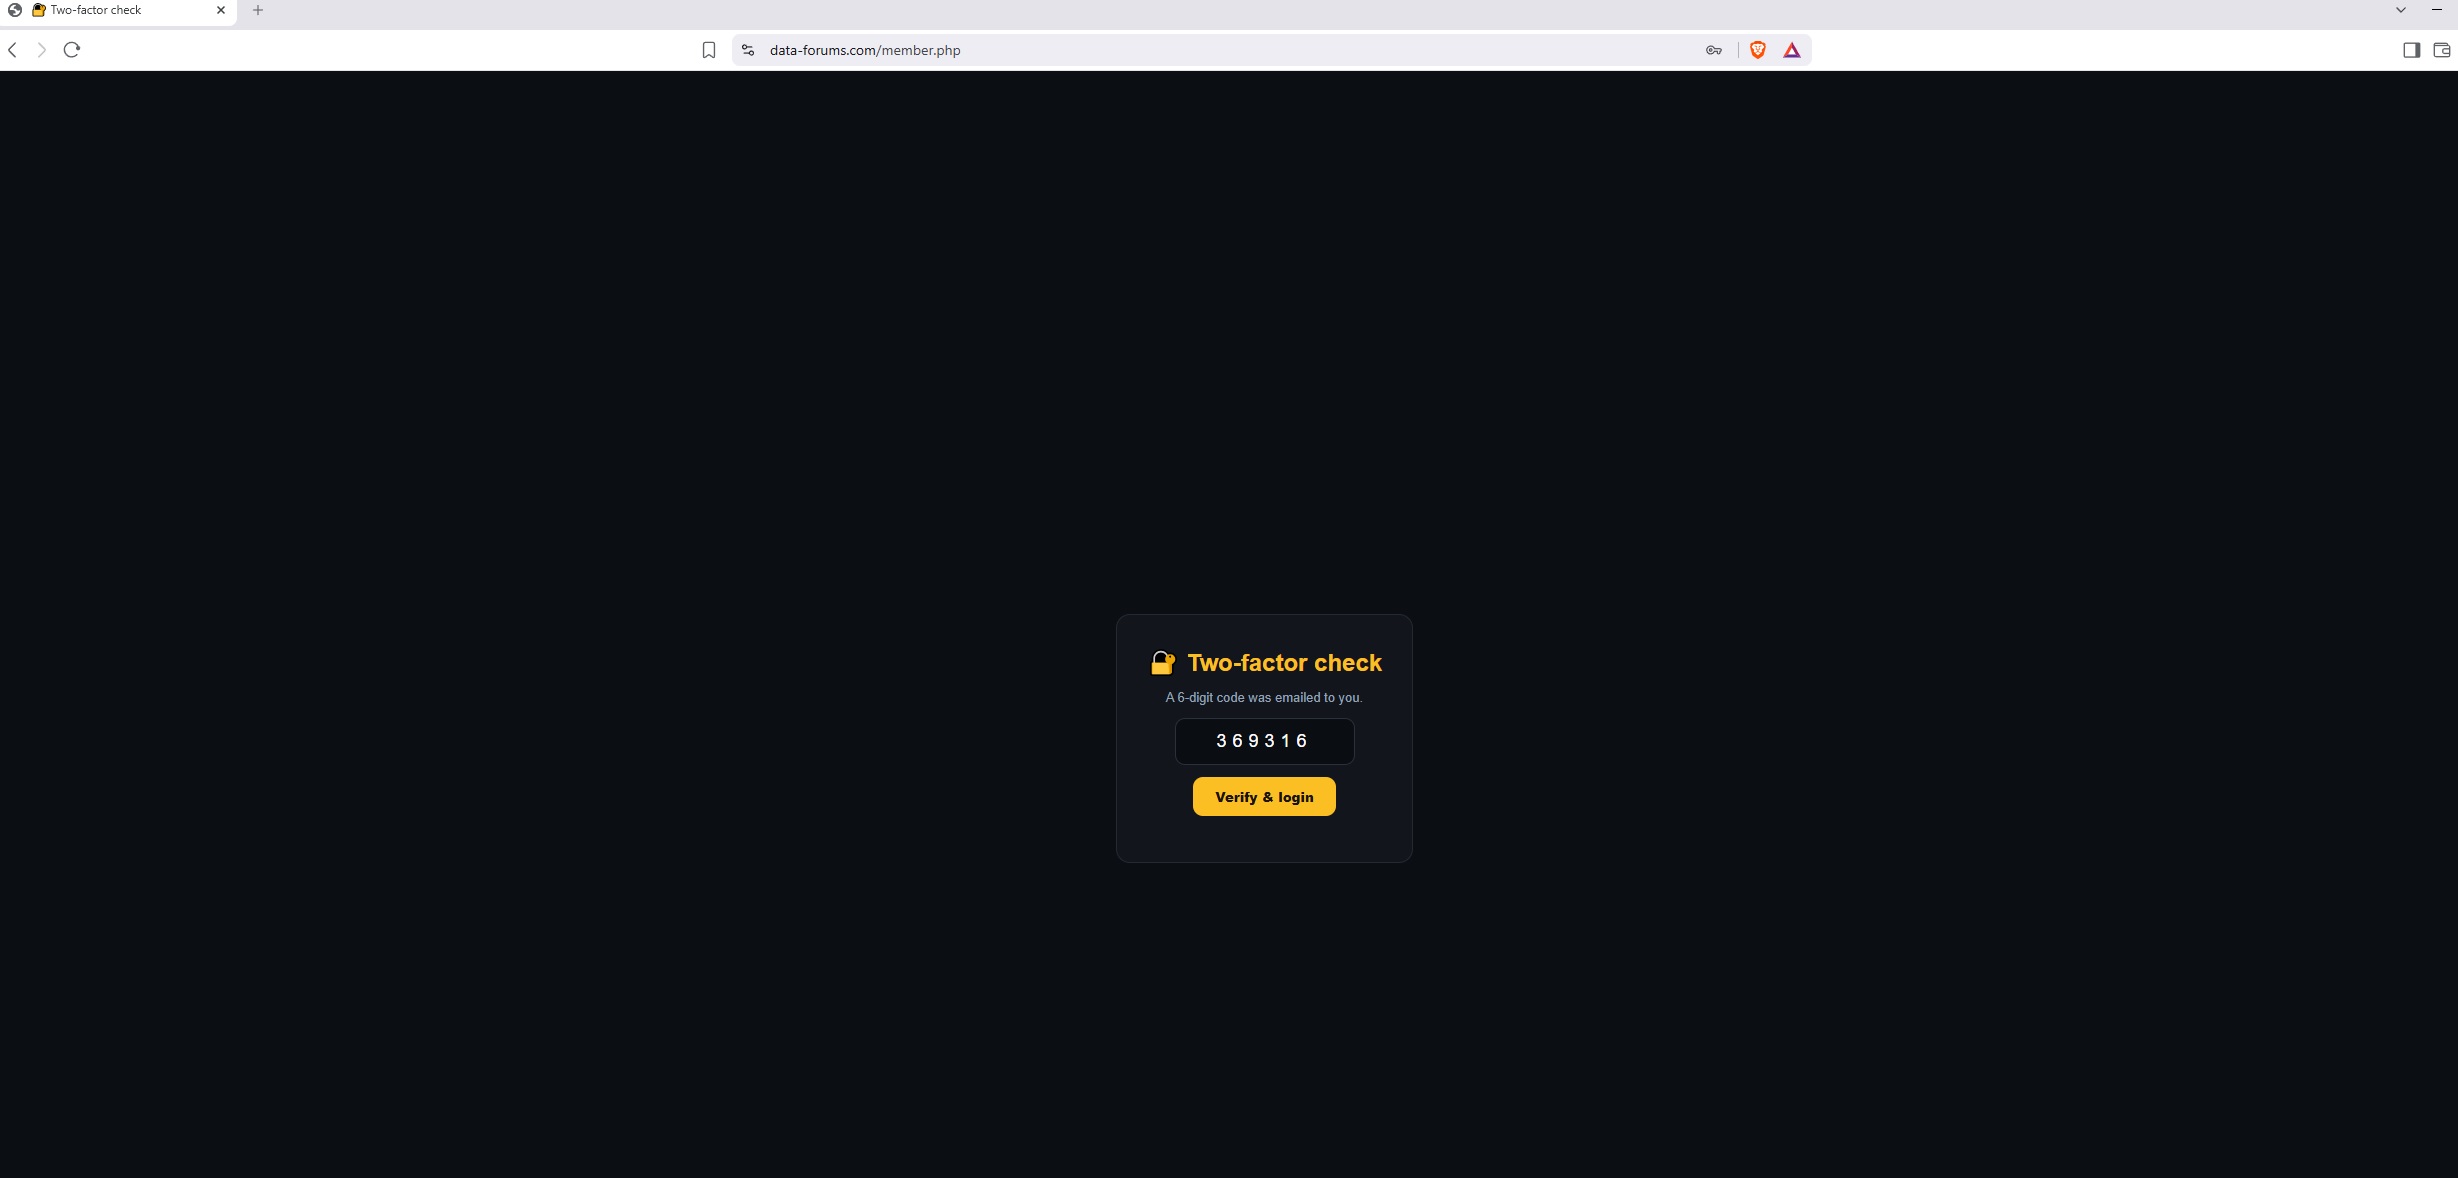
Use native member.php?action=login with a protected account. After a valid password, enter the emailed six-digit code. Normal unprotected members keep native login.Test evidence
21 browser/auth-flow assertions cover correct/incorrect code, no auth before OTP, CSRF, expiry, replay, session transfer, credential change, cancellation, attempts, HTTP refusal, delivery failure and ordinary-member login. Additional PHP checks cover protected primary/additional groups.
The eight-release wave passed 117 scoped assertions across PHP/MyBB, browser, HTTP and lifecycle checks. Some tests used a combined plugin context; this is not a universal compatibility certificate or an independent security audit.
Limitations / breaking changes
Protects native forum login completion, NOT the Admin CP login or SSO plugins that set authentication cookies directly. Preserve and test separate ACP/SSO security. Email delivery was exercised through a lab capture adapter, not your real SMTP provider. Third-party CAPTCHA/login integrations need staging checks. This is not an independent security audit.
Deactivate / uninstall
Deactivate retains settings/challenges. Uninstall removes the new challenge/key tables and its settings, invalidating pending challenges; it does not delete accounts or posts.
Changelog
2.0.0 — 21 October 2026: Security-focused replacement for the recovered 1.2 distribution. Full source, README, upgrade notes, changelog, test-scope note and licence included in the ZIP.
Download the current Vault release — existing access rules apply.
Support / licence
Reply below or PM Sir-Vigu (uid 1) with versions and a minimal reproduction. Never publish credentials or private member data. GPL-3.0-or-later; existing attribution retained.
Full verification register
Original release notes
🔐 DF Login OTP v1.2
Bank-style email two-factor for your staff logins - 🎁 FREE for all members
🔧 What it is
Email two-factor authentication for the logins you choose (admins/mods by default). A stolen password is worthless without the inbox. Everyone else logs in exactly as before.
🔁 How it works
- Protected member submits username + password (full form OR header quick-login - both supported)
- Password verified server-side; a 6-digit code is e-mailed (CSPRNG), hashed into a 15-minute cookie, 60s cooldown
- The OTP form carries a signed, AES-256 encrypted, time-limited token - the password NEVER renders in the DOM
- Correct code -> hash_equals verification -> core login completes
- random_int() codes + hash_equals everywhere
- AES-256-CBC encrypted password token with expiry + signature
- Rate-limited code e-mails
- Zero plaintext secrets in HTML
- Clean uninstall (settings + templates removed)
🏗️ Structure (reviewer standard)
Lifecycle-only main file · hooks.php · handlers.php · permissions.php · db.php (schema-less, documented) · settings.json/php (insert_query_multiple) · templates.json/php · external stylesheet · English + ACP language packs.
📦 Inside
Full plugin tree - download from the DF Vault button below.
🛠️ Install
- Upload the tree preserving paths
- ACP -> Plugins -> DF Login OTP -> Install & Activate
- Settings -> DF Login OTP -> set protected group IDs (default 3,4)
- 1.2 - AES-encrypted token, quick-login support, mail interpolation fix, CSPRNG codes, rate limiting, reviewer-standard structure (board-tested first!)
- 1.1 - standardized multi-file build
- 1.0 - first release
Reply here or PM Sir-Vigu.
A Data-Forums free release - tested on ourselves before sharing. data-forums.com
👍 Like0❤️ Love0😂 Haha0🔥 Fire0👏 Clap0⚡ 0
Sir-Vigu
Founder, Data-Forums.com
Connecting data professionals, ideas, and innovation.
Founder, Data-Forums.com
Connecting data professionals, ideas, and innovation.